
LDAP Vs. RADIUS
LDAP and RADIUS are often mentioned together because both can play a role in user authentication, but they solve different problems.
LDAP, or Lightweight Directory Access Protocol, manages and retrieves identity information from a directory. RADIUS, or Remote Authentication Dial-In User Service, is designed to authenticate and authorize access to networks and services.
This article walks administrators through selecting the best solution for their network requirements by exploring LDAP and RADIUS’s unique features and relative strengths. Understanding the complexities of these protocols is critical for creating strong and secure authentication processes inside organizational infrastructures.
What Is the Difference Between LDAP and RADIUS?
LDAP is a directory service that stores and organizes information about users, groups, devices, and other identities. RADIUS handlesauthentication and authorization when users or devices request access to Wi-Fi, VPNs, or wired networks.
The table below illustrates some of the key differences between LDAP and RADIUS.
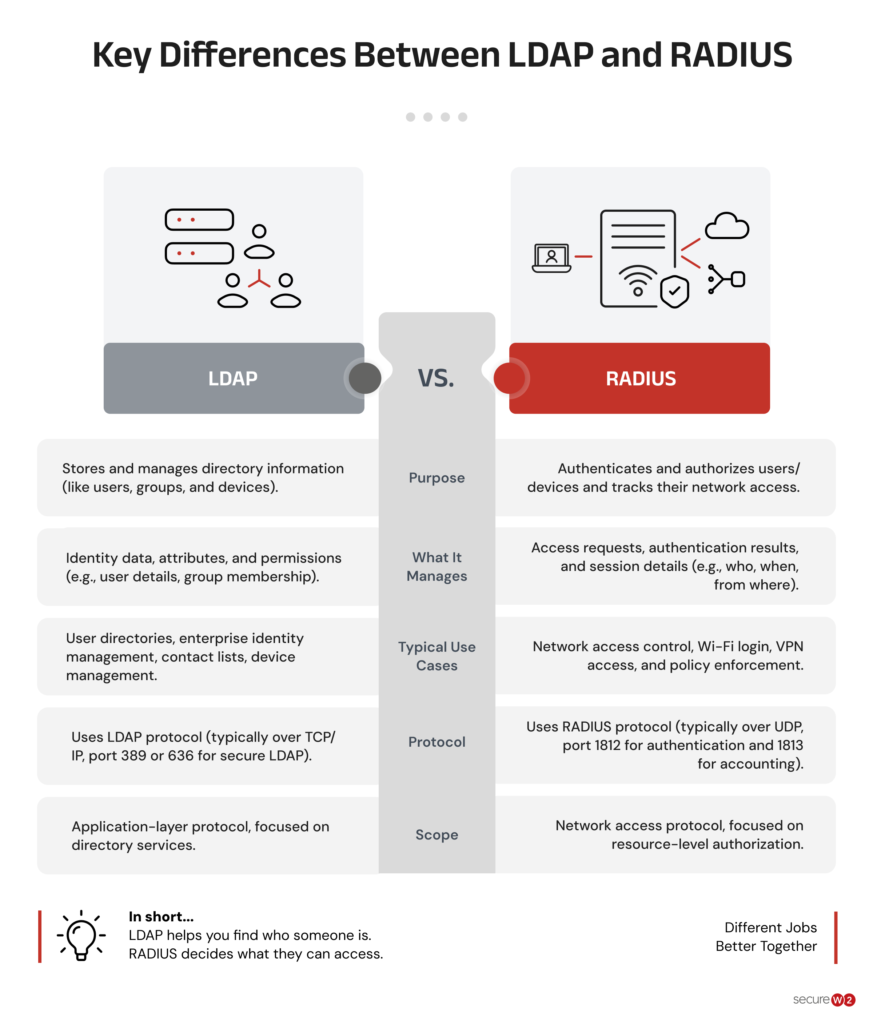
LDAP can provide identity information and answer questions such as who a user is and which groups they belong to, while RADIUS uses that information to decide whether a user or device can access the network.
What Is LDAP (Lightweight Directory Access Protocol)?
LDAP is a software protocol that enables servers to look up data stored in on-premises directories. The “data” can be information about organizations, devices, or users.
The following diagram illustrates the LDAP authentication process.
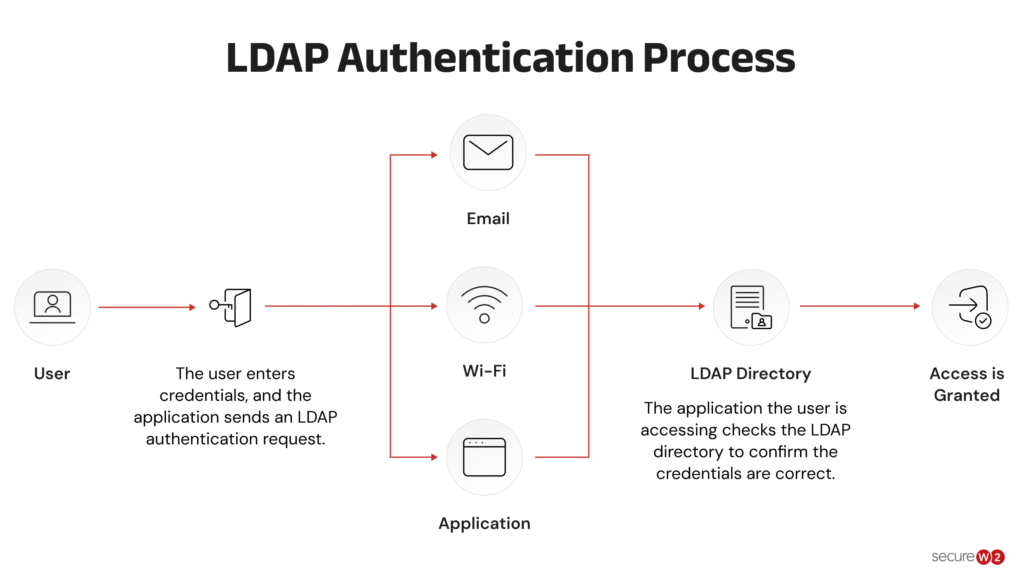
Data is stored in a hierarchical structure called a Directory Information Tree (DIT), which organizes data into a branching “tree” structure, making it easier for admins to navigate their directories, find specific data, and administer user access policies.
What Is RADIUS?
RADIUS is used to authenticate the user and their device and authorize them for network access. The authentication and authorization process occurs each time a user reconnects to the network, taking the guesswork out of determining who is using your network.
The diagram below illustrates how the RADIUS authentication flow works.

RADIUS can authenticate credentials, one-time passwords (OTPs), and hardware security keys.
Success: Using a RADIUS server is an effective way to boost network security and visibility.
It is especially effective when configured properly with certificates, which we will delve into in the next section.
To learn more, see our detailed guide on RADIUS authentication, and watch our video on how a RADIUS server works.
LDAP vs. RADIUS: Key Differences
LDAP and RADIUS can work together, but their roles are different. LDAP provides access to identity and directory data, while RADIUS controls network authentication and authorization.
This table explains the key differences between RADIUS and LDAP.
| Feature | LDAP | RADIUS |
|---|---|---|
| RFC standard | RFC 4511 | RFC 2865; RFC 2866 for accounting |
| Primary role | Access and manage directory information | Network authentication, authorization, and accounting |
| Transport protocol | TCP; LDAP commonly uses 389, LDAPS 636 | UDP traditionally; TCP/TLS and DTLS are also defined |
| Ports | 389 for LDAP, 636 commonly for LDAPS | 1812 for authentication, 1813 for accounting |
| Encryption scope | TLS can protect the LDAP connection | Traditional RADIUS protects selected attributes and uses shared secrets; RADIUS/TLS or DTLS can protect the transport |
| Accounting support | No built-in AAA accounting function | Yes, through RADIUS Accounting |
| Database requirement | Requires a directory service to provide directory data | Can use an external directory, identity provider, database, or certificate infrastructure |
Also Read: How to Set Up Certificate-Based WPA2-Enterprise with LDAP
Similarities Between LDAP and RADIUS
LDAP and RADIUS have different primary roles, but they can appear in the same enterprise authentication architecture. This table explains the similarities between them.
| Feature | LDAP | RADIUS |
|---|---|---|
| RFC standard | RFC 4511 | RFC 2865; RFC 2866 for accounting |
| Primary role | Access and manage directory information | Network authentication, authorization, and accounting |
| Transport protocol | TCP; LDAP commonly uses 389, LDAPS 636 | UDP traditionally; TCP/TLS and DTLS are also defined |
| Ports | 389 for LDAP, 636 commonly for LDAPS | 1812 for authentication, 1813 for accounting |
| Encryption scope | TLS can protect the LDAP connection | Traditional RADIUS protects selected attributes and uses shared secrets; RADIUS/TLS or DTLS can protect the transport |
| Accounting support | No built-in AAA accounting function | Yes, through RADIUS Accounting |
| Database requirement | Requires a directory service to provide directory data | Can use an external directory, identity provider, database, or certificate infrastructure |
How Does the LDAP Protocol Work?
LDAP authentication typically follows these steps:
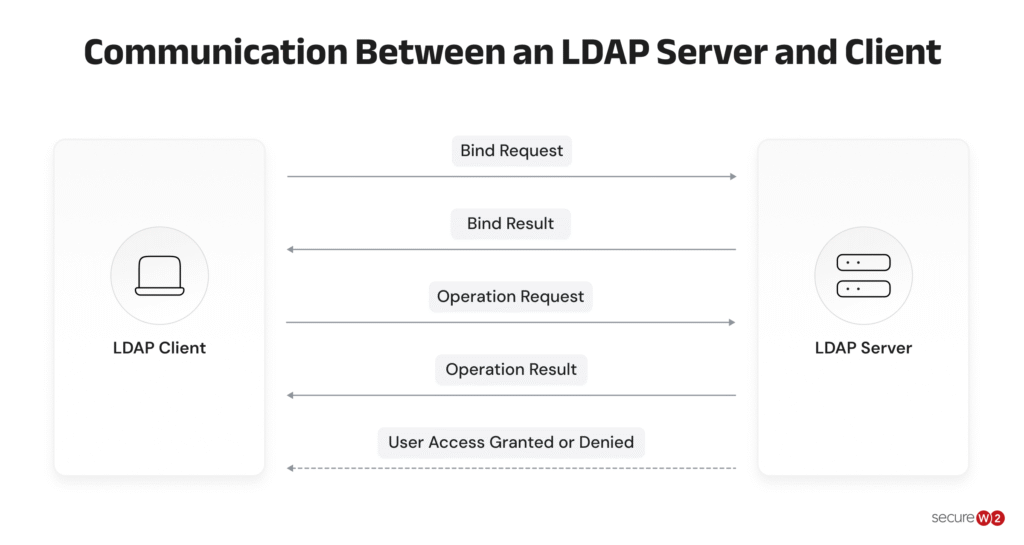
- The client connects to the LDAP server. The application or service establishes an LDAP connection with the directory.
- The client sends an authentication request. The client can use an LDAP bind to submit a user’s distinguished name and credentials.
- The LDAP server validates the credentials. The server checks the supplied information against the directory.
- The directory returns the result. The server confirms whether authentication succeeded or failed.
- The application retrieves identity data. After authentication, it can query attributes such as group membership, department, or access-related information.
- The application makes an access decision. The application or service uses the returned identity information to determine what the user can access.
The following image illustrates the communication flow between an LDAP server and client.
What Is LDAP Used For?
LDAP is used for accessing and managing directory information over a network.
Info: The protocol lets applications look up and authenticate against a centralized directory of information, usually about users, groups, and resources in an organization.
Here’s what LDAP is typically used for.
Common use cases of LDAP:
- User authentication: Verifying login credentials against a central directory, like logging into a company’s Wi-Fi, VPN, or internal apps
- User/group management: Storing and organizing information about employees, their roles, group memberships, and permissions
- Address books: Storing contact info like names, emails, phone numbers, and job titles that other applications can look up, such as corporate email clients
- Single sign-on (SSO): Acting as a backend directory that multiple applications check against, so users don’t need separate credentials for each system
- Access control: Determining what resources a user can access based on their group membership or attributes stored in the directory
Risks of the LDAP Authentication Protocol
- LDAP traffic over port 389 can be unencrypted, exposing credentials and directory data. Use TLS to secure the connection.
- Password-based LDAP authentication can increase the risk of phishing, password theft, and credential reuse.
- Poor input validation can allow LDAP injection attacks that manipulate queries and access unauthorized directory data.
- Improper directory permissions can expose sensitive user and group information.
- Traditional LDAP deployments require organizations to manage servers, connectivity, backups, and security controls.
Is LDAP an AAA Server?
Not by itself. LDAP is primarily a directory access protocol.
Info: LDAP can authenticate users and provide information used for authorization, but it does not natively provide the complete network access workflow associated with an AAA server.
RADIUS was specifically designed to handle authentication, authorization, and accounting for network access. LDAP can serve as a user directory that a RADIUS server queries during authentication, but LDAP and RADIUS are not interchangeable.
How Does the RADIUS Protocol Work?
In summary, to authenticate a user:
A RADIUS client notifies the RADIUS server via a RADIUS Access-Request message. The Access-Request message contains the user credentials.
The RADIUS server receives the request, checks the credentials against the user database, and then sends back one of three replies:
- Access-Accept: Approves the user’s attempt to log in.
- Access-Reject: Dismisses the user’s attempt to log in.
- Access-Challenge: Provides the user with an additional challenge, such as requesting a code entry.
Info: RADIUS enables accounting in addition to authentication and authorization.
A Comparative Analysis of RADIUS vs. LDAP in Network Security
LDAP and RADIUS can both be part of an enterprise authentication architecture, but they serve different roles.
LDAP provides access to directory information and can validate user credentials, while RADIUS is designed to authenticate and authorize network access.
LDAP answers questions about identity and directory information. RADIUS handles network access requests and can return authentication and authorization decisions.
Authentication Dynamics: RADIUS vs. LDAP
- LDAP typically authenticates users against a directory using credentials such as a username and password.
- RADIUS supports multiple authentication methods and is commonly used with 802.1X, VPNs, MFA, and certificate-based authentication.
RADIUS can also work with a PKI to authenticate digital certificates rather than relying only on passwords. With 802.1X, server certificate validation helps devices verify that they are communicating with the intended authentication server before sending authentication credentials.
Info: For enterprise Wi-Fi and other network access scenarios, certificate-based authentication with RADIUS can reduce reliance on passwords and provide stronger device and user authentication.
Another important distinction is where identity information is stored. RADIUS does not function as a directory. Instead, it can connect to an external identity provider, LDAP directory, database, or other identity source to validate authentication requests.
Scalability in RADIUS Server vs. LDAP Server
LDAP and RADIUS can both be deployed at scale, but they serve different infrastructure needs.
- LDAP is primarily used to maintain and provide access to directory information.
- RADIUS handles authentication and authorization requests for network access.
Cloud-based RADIUS can reduce the need to maintain dedicated RADIUS servers on-premises and can support distributed environments without requiring organizations to operate their own authentication infrastructure.
Can RADIUS Use LDAP?
Yes. RADIUS can use LDAP as an identity source.
In this setup, the RADIUS server receives an authentication request and queries the LDAP directory to validate the user or retrieve identity information.
For example:
User/device → Network → RADIUS → LDAP → RADIUS → Access decision
RADIUS-backed certificate authentication does not require LDAP, but organizations can use both when their existing directory remains the source of user information.
Microsoft Active Directory is a common example of an LDAP-compatible directory used alongside RADIUS. This allows organizations to retain their existing directory while using RADIUS for network authentication.
Note: Using LDAP with RADIUS does not make LDAP itself a RADIUS server. Each protocol continues to perform a different role in the authentication process.
Move Beyond On-Premises RADIUS With a Cloud-Native Authentication Stack
On-premises RADIUS servers carry hefty maintenance costs and an increased risk of hardware failure.
Our Cloud RADIUS eliminates operational overhead while strengthening security.
It authenticates users and devices using live security signals from your identity provider, MDM, and EDR/XDR platforms, so access decisions reflect current device posture, not a stale snapshot from last week’s sync.
The result is authentication that scales with the organization, not against it. Teams that have replaced legacy RADIUS with SecureW2 Cloud RADIUS consistently report faster authentication times, fewer outages, and best-in-class uptime, and the option for 99.999% availability.
If your current RADIUS setup is creating friction for IT or leaving security gaps, there is a better path. See SecureW2 Cloud RADIUS in action.
Frequently Asked Questions
Is RADIUS the same as LDAP?
No. LDAP is a directory access protocol, while RADIUS is a network authentication and authorization protocol. LDAP manages and retrieves identity information from a directory. RADIUS receives network access requests and determines whether they should be accepted or rejected. They can work together when a RADIUS server uses an LDAP directory to validate user identities.
Is RADIUS still used today?
Yes. RADIUS remains widely used for enterprise Wi-Fi, VPN authentication, 802.1X, and network access control. The protocol has also evolved beyond its original UDP-based implementation, with standards supporting secure transports such as RADIUS/TLS and RADIUS/DTLS.
Is LDAP outdated?
No. LDAP is still widely used for directory services and application authentication. The protocol itself is not obsolete. However, organizations should secure LDAP deployments with appropriate encryption and access controls, and evaluate whether password-based authentication remains suitable for their security requirements.
What does LDAP stand for?
LDAP stands for Lightweight Directory Access Protocol. It is a protocol for accessing and managing information stored in directory services, including users, groups, devices, and other organizational resources.
